Technology Due Diligence for Mergers & Acquisitions
Understand the technology risk, required investment, and transition work before it affects the deal — or becomes a post-close surprise.
Technology costs may show up in the financials, but the condition, risk, dependencies, and future investment behind those numbers usually do not. A server nobody documented. A vendor agreement tied to terms nobody reviewed until after signing. An account only the departing owner can access. Integration costs nobody priced in because nobody knew to look.
Which situation fits you?
Which situation are you in?
Buy-sideWhat are we acquiring, what could surprise us, and what will it cost to address?+
You want to know whether the technology will support the deal — or quietly erode EBITDA, increase post-close spend, create execution drag during the hold period, or complicate a future exit. That means technical debt, security gaps, licensing and vendor commitments, and control of critical accounts and systems. We present the findings in business terms that can inform valuation, negotiation, and post-close planning.
Sell-sideWhat will a buyer find, and what should we address or disclose before diligence begins?+
Before a buyer finds a problem, you want to find it first — including accounts, licenses, and vendor arrangements that may not transfer as expected, and technical debt that could hand a buyer negotiating leverage. A clean technology story protects value; a messy one becomes a bargaining chip.
Post-closeWhat needs to happen in the first 100 days to stabilize, integrate, or modernize?+
The work doesn't end at signing. The findings from diligence become the starting point for a first-100-days roadmap covering account and domain transfer, vendor relationships, stabilization, integration, and modernization.
What we look at
Depending on which situation applies, this can include:
01Infrastructure, security & data+
- Infrastructure age and condition
- Cybersecurity controls and readiness for identified compliance requirements
- Data privacy controls
02Licensing, contracts & ownership+
- Software licensing, transferability, and vendor commitments
- Contract terms that may require deal-counsel review
- Account and domain ownership
- Vendor concentration
03People, documentation & integration+
- Key-person dependence
- Documentation quality
- Integration cost and complexity
04Transition & separation readiness+
- Day-One operating requirements
- Systems requiring separation or migration
- First-100-day sequencing
How we validate what we find+
We validate the picture through management interviews, technical and access review, documentation and account-ownership validation, licensing and vendor-document review, and — where access allows — direct review of critical systems and controls. We also flag where deeper technical or cybersecurity diligence is warranted — and where it isn't, so effort stays proportionate to the deal.
Assessments are led by Jean Prejean, Principal, CISA and CISM certified, with project execution led by Wayne Speziale, Director of Operations, a certified Project Management Professional (PMP).
What diligence can uncover
Missing multifactor authentication, aging infrastructure, and control gaps relevant to HIPAA — found before close, while the buyer could still act on them.
No multifactor authentication, no encryption, and financial and HR records held only on local USB drives — no offsite backup anywhere.
What you receive
A structured due diligence report built for business and transaction decisions — not a raw technical printout.
Decision-ready findings
✓Findings by priority+
Rated high, medium, or low based on business impact and likelihood, not technical severity alone.
✓Visual risk heat map+
Showing where risk clusters by potential impact and likelihood, so the most important concerns stand out at a glance. An illustrative example appears below.
✓Confidence ratings+
How reliable the underlying information is for each finding, including where conclusions depend on limited access, incomplete records, or self-reported information.
✓Assumptions and limitations+
A straightforward explanation of what the review could and could not confirm, what access was available, and where uncertainty remains.
Action and investment planning
✓Cost and priority table+
Rough order-of-magnitude cost ranges tied to each finding, separated into one-time and ongoing costs, with the confidence level behind each estimate.
✓Prioritized recommendations+
Tied directly to the findings and cost table, with guidance on what should happen before close, soon after close, or later.
✓Deal and transaction implications+
A plain-language explanation of how findings may affect valuation, closing conditions, operational continuity, or post-close investment.
The report gives the deal team — IC, operating partners, and boards — a decision-ready view of technology risk, likely investment, and unresolved questions that may affect diligence, closing, or post-close planning.
What the risk heat map looks like
Illustrative example. Your report reflects what we actually find in the environment.
Execution support
Beyond the diligence report
A report is the starting point, not always the finish line. Depending on the transaction, we can also help:
Day-One planning
Building the plan and sequencing first-100-day priorities.
Separation & integration
Doing the work directly, not just scoping it.
Ownership transfer
Administrative control, domains, and vendor accounts.
Urgent remediation
Fixing what can't wait, before or after close.
Interim oversight
Technology leadership through the transition.
This turns findings into execution, without compromising the independence of the diligence itself.
Why timing matters
A gap found in diligence can shift price, timeline, or terms. The same gap found six months after close is just a cost you're already carrying.
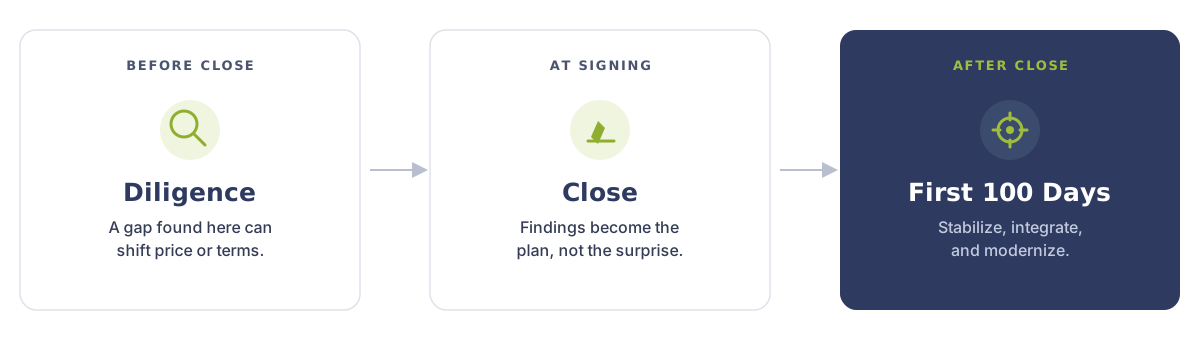
Diligence. A gap found here can shift price or terms.
Close. Findings become the plan, not the surprise.
First 100 days. Stabilize, integrate, and modernize.
Ready to understand the technology behind the deal?
Tell us where you are in the process, and we'll scope the review to fit the deal.
What this isn't. This is technology and cybersecurity due diligence — not a business valuation, legal opinion, financial audit, compliance certification, or interpretation of contract enforceability. We identify and validate the technical and operational facts the broader deal team needs, working alongside valuation, legal, financial, and compliance advisors rather than replacing them.